A firsthand account of what earning CMMC Level 2 revealed about automation, evidence, and what compliance actually costs.
Everyone treats compliance and speed as opposites. The math on our own CMMC Level 2 assessment says otherwise — and the seven months it took to get there is the receipt.
Numbers worth counting
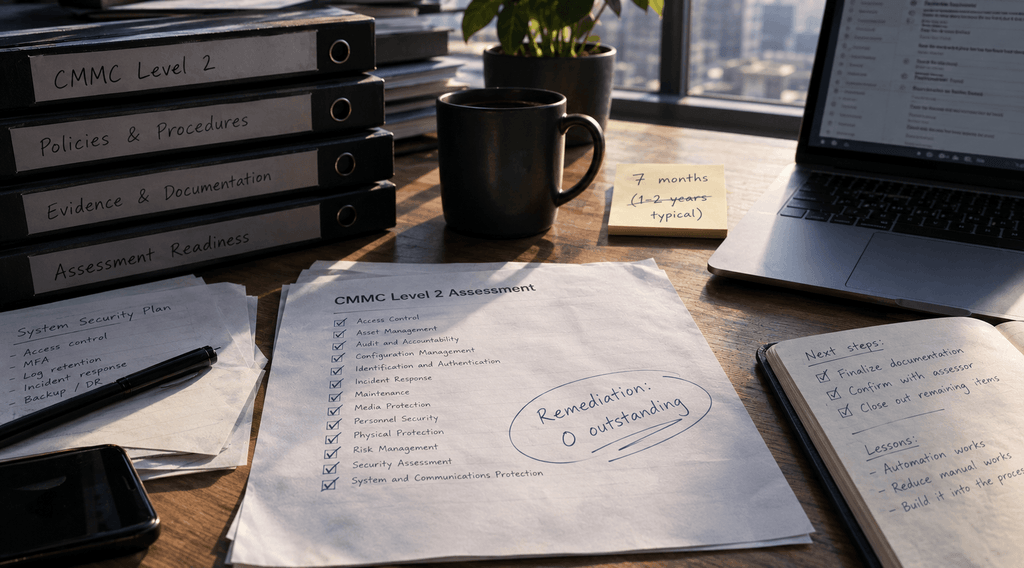
A CMMC Level 2 certification program typically takes an organization one to two years. Ours took seven months, and was completed with no outstanding remediation.
Almost all of the cost in a compliance program is labor, most of it people proving by hand what their systems already record. That is the whole explanation for seven months. Not that we were clever, and not that the assessment was easy. We had already changed what evidence costs to produce. Reduce that cost, and the timeline collapses. If you do not change how evidence is produced, more budget mostly scales the same labor problem.
That is a claim about operations. The established framing is that compliance is a tax on velocity. This gets the causality backwards.
A premise worth considering
Harish Luthra, the CEO of SAP NS2, was asked recently whether compliance slows innovation down. His answer was that it depends entirely on where you put it. “If we say it’s an IT function, and we have to make sure IT has CMMC compliance across the entire organization, then it will slow everything down.” But when it is built into how the work is done rather than inserted at checkpoints — “part of the end-to-end process versus inserting security or compliance in certain milestones” — the tax disappears. His report on the result is blunt: “We’ve not seen it slow down anything in our organization.”
NS2 is a useful vantage point for this. It is wholly owned by SAP but operates as a proxy organization governed by the Defense Counterintelligence and Security Agency, serving defense, government and critical infrastructure customers. Its tagline, in Luthra’s words, is “Protect what matters, but drive what’s next.”
He names three things that make this real rather than rhetorical. Be honest about where you actually stand — NS2 brought third-party assessors in specifically to surface “vulnerabilities … holes that we need to fill,” and then took the findings seriously. Put executive ownership behind it: “I have personally taken on the securities executive sponsorship within the organization.” And unify your controls, so that “both the internal corporate controls and the customer controls are both exactly the same.”
The last of the three is where we pick up, because in our corner of the industry it is not an aspiration to work toward, it is a structural fact you cannot escape.
A view from one layer down the stack
Apiphani exists to run mission-critical estates for some of the most complex regulated organizations in the world: SAP, the databases and operating systems beneath it, ITSM, the data platforms alongside it, from the hypervisor up through the application layer. When a regulated organization hands us that estate, our administrators hold privileged access to the systems their regulated data lives in. We are not adjacent to their compliance boundary. We are inside it.
Apiphani holds internal and external standards to the same line — not as a policy preference, but because they are the same standards applied to the same systems. Any gap between how we secure ourselves and how we secure our customers is not a policy inconsistency, it is a live exposure in somebody else’s audit.
“There’s no version of this where we hold ourselves to a lighter standard than we hold our customers to. Our access to their systems is their exposure. So unifying the controls isn’t a compliance decision, it’s the only operating model that makes sense once you understand where the risk actually sits.”
— Justin Folkers, Co-Founder & CEO, apiphani
This is the part of the compliance conversation that tends to go missing. The attention goes to whether the DIB prime is certified. Considerably less goes to whether the organization with root on the prime’s ERP system is. For most of the last few years that second question had an uncomfortable answer across the industry, back when self-attestation was the norm; this is a large part of why so many mid-market manufacturers found themselves choosing between carving their provider out of scope and pulling the work back in-house.
Seven months
What made our timeline possible is that the automation running in the estate was already producing the record. Apiphani exists because managing environments at density manually does not work; our approach autonomously prevents incidents, handles patching and configuration drift, and does so continuously rather than in scheduled batches. The audit trail is a byproduct of our operating model, not a separate project stood up to satisfy an assessor.
When the assessor asked whether our configuration management was real, the answer was not a policy document and a sample of change tickets assembled for the occasion. Much of the evidence already existed as machine-generated operational records — produced by the systems that run configuration management, not reconstructed after the fact.
Where the friction lives
Once understood, the familiar tension between compliance and velocity resolves as a tension between compliance and traditional, manual operations.
If access reviews are a quarterly spreadsheet exercise, every additional control genuinely does slow the process down, and the organizations that describe security as a blocker or drag on delivery are reporting their reality. But if entitlement is enforced by the system, if elevation is time-bound and recorded automatically, if drift is detected and corrected without a ticket, then the control is not competing with velocity. It is a fundamental component of how the work gets done at all.
When the Pentagon suspended CMMC Phase II in July, the reasoning was blunt. The Department’s CIO, Kirsten Davies, said the math “just simply doesn’t math for small to medium-sized businesses to even get compliant by the transition date.” Behind that: roughly one hundred certified assessors against more than one hundred thousand contractors, and a compliance burden estimated in the billions annually falling hardest on small and mid-sized businesses.
It is worth pointing out where that burden sits, because it is not mainly the assessment. The government’s three-year estimate for a CMMC Level 2 assessment is substantial on its own, but it assumes the 800-171 controls are already implemented and excludes the cost of getting there. The larger number is upstream.
In the FAR CUI rulemaking the government models a small contractor’s first year at roughly $175,700, with $148,200 of that labor, against $27,500 of hardware and software, and each year after at about $103,800, of which $98,800 is labor. Across three years, more than ninety percent of the cost is people.
Assessments consume so much assessor time because most of the evidence being examined is produced by hand, is inconsistent across a contractor’s estate, and has to be sampled and interrogated accordingly.
Compliance delivers downstream value
Our customers can rely on controls we already operate and evidence, rather than recreating equivalent capabilities inside their own operating model. The alternative is rebuilding the capability in-house, which is the first-year labor bill above plus the recurring cost of operating it. Inheriting a control you can evidence is not merely more convenient than rebuilding it. It is a different order of expense.
Evidence arrives on your timeline, not ours. In most provider relationships, an evidence request from your auditor triggers a scramble: someone assembles a bespoke package over several weeks, often differently for each customer who asks. When the record is generated continuously as a byproduct of operations, producing it is closer to running a query than running a project. Your audit calendar stops depending on our availability.
Patching stops competing with change control. Regulated organizations often patch slowly, not because they disagree about the risk but because their change process is heavy. When change is enforced and recorded by the system rather than gated by a committee, speed and control stop trading against each other. You can move faster and prove it afterwards.
A new environment inherits the posture on day one. Because our controls are properties of the platform rather than terms negotiated per engagement, adding an environment or onboarding a new workload does not reopen the compliance conversation from the beginning.
The incident reporting clock is protected. DFARS 72-hour reporting flows down to you, and a provider who discovers things late makes that deadline yours to miss. Automated detection is what keeps our notification inside your window rather than at the edge of it.
Validation of a process is not a final measure
We hold CMMC Level 2, ISO/IEC 27001:2022, SOC 2 Type II and CSA STAR Level 1 certification. They answer different questions, and none of them substitutes for another.
- Overlap is real but partial. The overlap with ISO 27001:2022 is meaningful but partial; an ISO certification does not satisfy a CMMC assessment. Each covers ground the other leaves open.
- Scope is everything. An assessment certifies a boundary, not a company. We do not publish ours, but we will walk any customer or prospect through it under NDA, because a scope you cannot inspect is a scope you should not rely on.
- A framework is not an outcome. None of this means we will never have an incident. It confirms that the controls are real, tested by an accredited independent third party subject to formal conflict-of-interest requirements.
What comes next
The CMMC Reform Task Force was due to report in mid-September 2026, with public release expected toward the end of the month or early October 2026. The likely outcomes range from a delayed restart to a narrowed scope in which third-party certification applies to fewer organizations and many move to enhanced self-assessment.
Programs get renamed and rescoped. The question underneath does not change: can you demonstrate, to somebody who does not work for you and does not want to be impressed, that the controls you claim are the controls you run?
If regulated data lives in an estate you have outsourced support for, that question is not yours alone to answer. So do not ask your provider which frameworks they hold. Ask them to show you the evidence, then ask what it cost them to produce it. If producing that evidence requires a project, bluntly you are already paying for that project, at their price and on your time. If it requires a query, the evidence is being produced by the operation itself.
Running regulated workloads through a provider — or wondering whether yours could survive that question?
References
Apiphani. (2026, September 1). Apiphani achieves CMMC Level 2, strengthening cybersecurity commitment for regulated industries. PR Newswire. https://www.prnewswire.com/news-releases/apiphani-achieves-cmmc-level-2-strengthening-cybersecurity-commitment-for-regulated-industries-302865778.html. Accessed September 17, 2026.
CMMC certification timeline: Costs, phases & what to expect. (2025, February 20). Coalfire Federal. https://coalfirefederal.com/resource/timeline-and-cost-insights-for-cmmc-compliance/. Accessed September 17, 2026.
Department of Defense, General Services Administration, & National Aeronautics and Space Administration. (2025, January 15). Federal Acquisition Regulation: Controlled Unclassified Information (FAR Case 2017-016; RIN 9000-AN56). Federal Register, 90 FR 4278. https://www.federalregister.gov/documents/2025/01/15/2024-30437/federal-acquisition-regulation-controlled-unclassified-information. Accessed September 18, 2026.
Department of Defense, Office of the Secretary. (2024, October 15). Cybersecurity Maturity Model Certification (CMMC) Program (Docket ID DoD-2023-OS-0063; RIN 0790-AL49). Federal Register, 89 FR 83092. https://www.federalregister.gov/documents/2024/10/15/2024-22905/cybersecurity-maturity-model-certification-cmmc-program. Accessed September 17, 2026.
Ross, R., Dempsey, K., & Pillitteri, V. (2018, June 13). Assessing security requirements for controlled unclassified information (NIST Special Publication 800-171A). National Institute of Standards and Technology. https://doi.org/10.6028/NIST.SP.800-171A. Accessed September 17, 2026.
Scoop News Group. (2026, July 20). Security involves more than checking boxes; it’s about accelerating defense innovation. DefenseScoop. https://defensescoop.com/video/how-security-compliance-accelerates-defense-innovation-sap-ns2/. Accessed September 17, 2026.
U.S. Department of War. (2026, July 13). Forging the arsenal of freedom: Department of War suspends CMMC Phase II requirements. War.gov. https://www.war.gov/News/Releases/Release/Article/4542329/forging-the-arsenal-of-freedom-department-of-war-suspends-cmmc-phase-ii-require/. Accessed September 17, 2026.
Vincent, B., & Easley, M. (2026, July 13). DOD halts cybersecurity requirements for CMMC Phase 2: “The math just simply doesn’t math”. DefenseScoop. https://defensescoop.com/2026/07/13/dod-halts-cmmc-cybersecurity-requirements-phase-2/. Accessed September 17, 2026.
Contact Us
- Tell us more about your business and what you need from automation and business software.
- One Financial Center
Suite 1640
Boston, MA 02111 - Request a Quote: +1 (833) 695-0811